
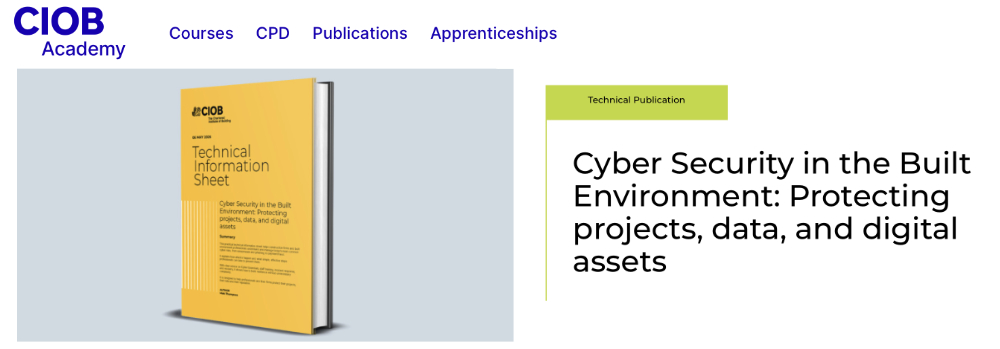
Cyber Security in the Built Environment: Protecting projects, data, and digital assets
[edit] About
Cyber Security is not just an IT issue; it is a business issue. With growing reliance on digital information and connected site technologies, cyber risks are evolving rapidly.
This Technical Information Sheet on cyber security provides built environment professionals with a comprehensive yet practical guide to today’s evolving cyber risks. From understanding threats such as ransomware and phishing to implementing core defence measures, it outlines clear, actionable steps to protect projects, data, and supply chains. As digital transformation accelerates, building cyber resilience is essential.
Cyber Security in the Built Environment: Protecting projects, data, and digital assets is suitable for built environment professionals to help understand and manage cyber security risks, protect projects, data and digital assets.
[edit] Summary
This practical technical information sheet helps construction firms and built environment professionals understand and manage today’s most common cyber risks, from ransomware and phishing to payment fraud.
It explains how attacks happen and what simple, effective steps professionals can take to prevent them.
With clear advice on Cyber Essentials, staff training, incident response, and recovery, it shows how to build resilience without unnecessary complexity.
It is designed to help professionals and their firms protect their projects, their data and their reputation.
[edit] Contents
[edit] Why cyber security matters in construction
| What do cyber incidents cost construction firms? | Proportionality and risk |
| Aim and Scope |
[edit] Understanding cyber security basics
| What is cyber security? | The construction sector’s unique cyber risk profile |
| Cyber security vs IT security |
[edit] The current threat landscape
| Ransomware | Supply chain vulnerabilities |
| Phishing emails | Assessing threats: ease, likelihood, and impact |
| Dark web and credential theft | Secondary impacts of cyber incidents |
| Insider threats | Real-world examples: cyber incidents and their impacts |
[edit] Core defence measures
| Cyber Essentials (and Cyber Essentials Plus) | Supply chain security |
| Strong authentication and access control | Cyber Security checklist for construction projects |
| Defences against phishing and BEC | Site-specific measures |
| Data and device protection | Quick wins |
| Backup strategy | Measuring effectiveness |
| Dark web monitoring | Common pitfalls to avoid |
[edit] Building cyber awareness and culture
| Staff cyber security training | A simple cyber security policy: what to include |
| Phishing simulations and practical exercises | Leadership and culture |
| Embedding a ‘report, don’t blame’ culture | Measuring awareness and culture |
| Creating and using a clear cyber security policy | Common pitfalls to avoid |
[edit] Testing, monitoring and continuous improvement
| Penetration testing | Regular audits and reviews |
| Vulnerability scanning versus pen testing | Continuous improvement |
| Security Operations Centres (SOCs) | Measuring success |
| Centralised logging and visibility | Common pitfalls to avoid |
[edit] Responding to incidents and recovering quickly
| Preparing for incidents: incident response planning | Legal, regulatory and communications considerations |
| Incident response in practice | Post-incident review and learning |
| Disaster recovery and DRaaS | Common pitfalls to avoid |
[edit] Building a sustainable cyber security strategy
| Making the business case for cyber security | What makes a strategy sustainable |
| Building a practical cyber security roadmap | Common strategic pitfalls to avoid |
| In-house vs outsourced cyber security: choosing the right model | Senior management checklist: building and maintaining cyber security |
| Using external support effectively |
[edit] Conclusion and next steps
| A practical action plan | Embedding cyber security into everyday business |
[edit] References
[edit] Further reading
[edit] About the Author
Matt Thompson is a freelance writer working in the UK’s construction industry, mainly for professional institutions, such as CIOB, RIBA and RICS.
He produces targeted content to meet organisational objectives; and has authored many publications, including the Guide to the DfMA Overlay to the RIBA Plan of Work (2021), PAS 8671:2022(the competence framework for individual Principal Designers under the Building Safety Act), and Handbook of Practice Management (2024). He is editor of the CIOB’s Construction Client Guide: Leading Projects in the Built Environment, Second Edition (2025).
Special thanks to Adrian Bell from LoughTec for providing the information on this topic.
[edit] CIOB Members
CIOB members can access Technical Information Sheets for FREE and receive a 20% discount on our Codes and Guides. Your discount codes are in the members’ portal. If you experience difficulties accessing the portal, contact lis@ciob.org.uk.
This article appears on the CIOB news and blogsite as "Cyber Security in the Built Environment: Protecting projects, data, and digital assets" from May, 2026.
--CIOB
[edit] Related articles on Designing Buildings
- Adapting your technology to the new working normal.
- CIOB Academy.
- CIOB articles.
- Cyber hygiene.
- Cyber resilience.
- Cyber security.
- Cyber security and engineering
- Cyber threats to building automation and control systems
- Cyber-physical system
- Cyber-security and phishing.
- Cyber security specialist.
- Infrastructure and cyber attacks
- Mitigating online risk.
Featured articles
Check out some of the best features and news from Designing Buildings as well as key stories from around the web.
CIOB celebrates positive Ofsted report.
The Building Safety Regulator announces a call for evidence.
Government approach could undermine delivery and regeneration.
World's first mass timber data centre.
The overlooked environmental aspect of data centre development.
Introduction to radon awareness
New technical information sheet published by CIOB.
Updated supplier guide can help electrical contractors engage with NHP.
CIAT confirm the winners of the 2026 architectural technology awards.
Government launches a one stop shop for flood preparedness.
Sir Edwin Lutyens: Britain's greatest architect? Book review.
CIOB publishes free template to help assess and manage risks.
ECA's reflections on Party Conference season
Burnham wants to be confident of winning before asking for a fresh mandate.
New Chief Construction and Scientific Adviser
Sergio Cavalaro, Professor of Infrastructure Systems at Loughborough University.